Bank of America's $1.2 billion penalty will be read as one large bank's failure. FinCEN's consent order is more useful than that. It shows a single alert threshold, set by judgement and kept in place because lowering it meant hiring hundreds of investigators, deciding for years what the bank was able to see.
On 13 October the Treasury announced penalties of more than $1.21 billion against Bank of America. FinCEN assessed $1.2 billion for wilful violations of the Bank Secrecy Act, crediting a separate $750 million civil money penalty from the Office of the Comptroller of the Currency, the largest the OCC has imposed. OFAC settled 475 apparent sanctions violations for $11.6 million. The bank admitted the wilful violations in the FinCEN order and neither admitted nor denied the OCC's findings. A day later it booked the cost as a $1.2 billion charge, not tax-deductible, in its third-quarter results.
The figure that will travel is the $5 billion: suspicious transactions the bank failed to report, or reported late, about $1 billion of them tied to what FinCEN calls priority national security risks. The more instructive material sits in the statement of facts. It describes, in detail regulators rarely publish, how the bank's monitoring system decided what got investigated from at least January 2018 to July 2025.
A line drawn by judgement and held by headcount
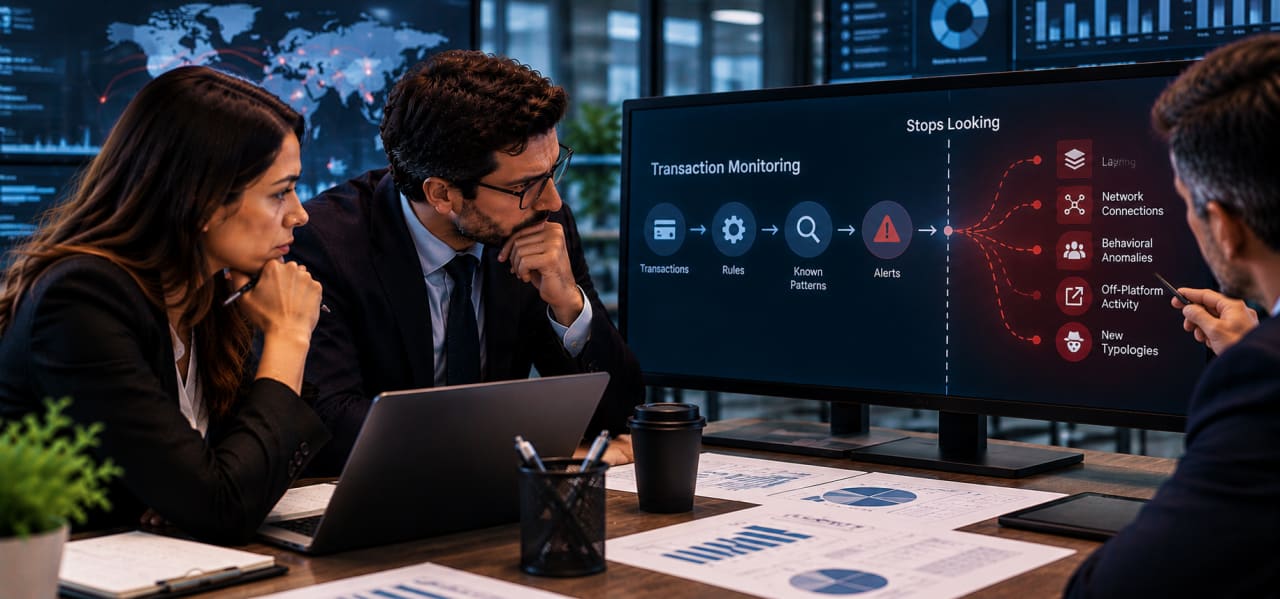
The system, which the order calls Event Processor, did not send individual alerts to investigators. It rolled them up, generally by customer, into "Event Groups" and added their weighted risk scores together. A group became a case only when it reached 20 points within 13 months of its oldest live alert. Below that line, nobody looked.
The threshold was, in the order's words, "initially set by stakeholder judgment". It stayed at 20 until December 2023. A 2022 model validation said its appropriateness "needs to be justified". A 2021 recalibration removed more than 8,200 cases from the investigation queue, and the accompanying report called the resulting "SAR loss" "permissible" without explaining how that was decided. When the bank tested a less constrained approach on samples from below the line, it found materially more reportable activity and turned the change down, reasoning that the "enormous below-the-line population" might "exhaust the investigation resources".
The price of moving the line is also on the record. When the bank finally cut the threshold to 10 or 12 points and shortened the window to four months, it estimated an extra 16,000 US investigations a month and an "incremental 750" staff to handle them, on top of 800 consultants for a one-time lookback. Even so, Treasury says, more than a year after the OCC's December 2024 cease-and-desist order the bank "still failed to escalate potentially suspicious activities to investigators for review".
A threshold that is never tested from below is a staffing plan with a risk label on it.
Most monitoring programmes, bought or built, have a line like this one: a score, a rule cut-off, a queue limit. It is often inherited from a vendor default or a launch-year assumption, and it is rarely revisited, because revisiting it creates work. FinCEN's complaint is not that the bank had a threshold. It is that the design "lacked empirical support" and that the bank "failed to establish an objective benchmark", such as a tolerance for false negatives, to judge it against. A 5% tolerance arrived only in December 2023.
Detection by other people's subpoenas
A quieter pattern runs through the case data. Some of the system's risk factors promoted a group straight to a case when something happened outside the model: a seizure warrant, a grand jury subpoena, an information-sharing request, an employee referral. The order says these "promote" factors produced more than a third of cases created from Event Groups, "peaking at nearly 50% in 2023". Treasury's conclusion was that the bank "effectively outsourced to third parties a substantial portion of its proactive detection and reporting obligations."
This is the paragraph a fintech should read twice. A young programme with a lightly tuned model will find much of its reportable activity the same way, through a sponsor bank's query, a 314(a) request or a spike in disputes. Those are legitimate inputs. Treasury's release says they cannot be "substitutes for their own effective internal monitoring and controls". A programme whose case volume rises and falls with outside requests is telling an examiner where its detection really happens.
The products that were never wired in
Coverage is the failure product teams own. Monitoring of negotiable instruments covered only certain purchases "and did not include any coverage of deposits". Between October 2020 and May 2025 two online auto-auction customers processed tens of billions of dollars in such deposits, and the bank failed to report suspicious money-order deposits of more than $600 million. The model built to catch cash structuring had gaps for credit cards until it was redeveloped in October 2024. A trade-based money laundering indicator built in January 2024 was not deployed to generate alerts during the period the order covers.
None of this is exotic. Each case is a product or channel that went live before monitoring caught up with it. Fintechs ship faster than most banks, and the interval between a product launching and its transactions reaching an active rule is exactly where this kind of exposure builds up.
Figure 1
What the order found | The question it puts to any programme | Where the answer usually sits |
|---|---|---|
A 20-point case threshold "initially set by stakeholder judgment", unchanged until December 2023 | Who set your threshold, on what evidence, and when was it last re-justified? | The model owner, if anyone has looked since go-live |
Below-the-line testing found more reportable activity; the change was rejected on resources | Do you sample below the line, and what happens when the sample finds something? | Model validation or the second line, often without a decision record |
A recalibration removed 8,200+ cases; the "SAR loss" was called "permissible" | When tuning cuts volume, who signs off on what is given up? | The head of financial crime, rarely in writing |
Up to half of cases started from outside events or referrals | What share of your cases begin with someone else's request? | Case-management data that is seldom reported |
No deposit coverage for negotiable instruments; credit-card gaps until October 2024 | Is every product and channel mapped to an active rule before launch? | Product and compliance, at launch review |
No false-negative benchmark until late 2023 | Have you written down how much missed activity you will accept, and how you would know? | Board risk appetite, where it exists |
Six findings, six questions. Findings summarised from the statement of facts in FinCEN Consent Order No. 2026-03. The question and "where the answer usually sits" columns are FinancyHub's editorial assessment, not survey data.
For builders, sponsor banks and the finance office
For founders and product leads, monitoring coverage now belongs on the launch checklist next to the licence and the ledger. A new payment type, card product or corridor needs a named rule set before its first transaction, not after its first outside query.
Sponsor banks are likely to push the same questions down the chain. Their examiners have just watched a supervised bank penalised over a threshold it could not defend, and the natural next request to a programme manager or fintech partner is to see theirs: threshold documentation, below-the-line results, a coverage map.
For the CFO, the order reframes an old budget argument. Investigative capacity is normally treated as a cost to contain, with alert volume as the thing that drives it. Bank of America's record shows the threshold staying where the team could cope. The bill arrived later: a $1.2 billion charge with no tax relief, a third-party lookback reaching back to January 2022, and independent reviews of its monitoring, due diligence and data governance. Finance does not set the threshold. It does set the headcount the threshold is quietly sized to, which makes the CFO party to the decision whether or not anyone says so.
Have these on paper before the next exam
The current case threshold or cut-off for each model, who approved it and the evidence they used.
The most recent below-the-line sample, what it found and what was done about it.
A written false-negative tolerance and the method for measuring against it.
A map of products and channels against the rules that cover them, with gaps dated.
The monthly share of cases opened from external requests or referrals.
For every recalibration that reduced volume, a signed record of what it was expected to miss.
An examiner's question used to be whether the monitoring system worked. After this order it is what the system was told not to look at, and who agreed to that.
Sources and notes. US Treasury press release, 13 October 2026 (coordinated FinCEN, OCC and OFAC actions; quotations on outsourced detection, external sources and post-2024 escalation). FinCEN news release and Consent Order No. 2026-03 against Bank of America, N.A., 13 October 2026; threshold, scoring, staffing, coverage and "promote" factor details are from its statement of facts, Relevant Time Period 1 January 2018 to 1 July 2025. OCC Order AA-ENF-2026-41, effective 13 October 2026, and OCC's description of the $750 million penalty as its largest, as reported by Wolters Kluwer VitalLaw (14 October 2026) and Al Jazeera (14 October 2026). Lookback scope (from January 2022) per VitalLaw's summary of the FinCEN undertakings. Third-quarter charge per Bank of America's results of 14 October 2026, as reported by MarketBeat and Fox Business. The OCC's December 2024 cease-and-desist order as described in the Treasury and FinCEN releases. FinancyHub has no commercial relationship with any firm named. Journalism, not legal, compliance or procurement advice. Corrections welcome.